As testing systems link IT and OT networks, traditional security models fall short, putting uptime, safety, and product integrity at risk.

Test system security insights
- Test systems have become high-risk gateways between IT and OT networks, making them prime targets for modern cyberattacks.
- Most vulnerabilities stem from outdated systems, expanded connectivity, supply chain risks and human error, all of which require coordinated mitigation.
- Long-term cybersecurity resilience depends on multilayered defenses, cross-team collaboration and adapting to emerging regulatory requirements.
The increased connectivity of devices, especially within industrial and research environments, has significantly enhanced the efficiency of test and measurement (T&M) systems. This interconnectedness, however, exposes a critical vulnerability: the rising threat of cyberattacks. In April 2024, the Fuxnet malware campaign demonstrated how destructive even rudimentary industrial control system (ICS)‑targeted cyberattacks can be. This malware targeted industrial sensor gateways by overwhelming communication protocols, disabling remote access, corrupting firmware and destroying memory, effectively rendering the attacked systems blind to real-time sensor data. Operational technology (OT) cyberattacks can cause operational shutdowns, product contamination or safety events when control logic is manipulated or hardware is mis-tested.
What makes test system cybersecurity particularly challenging is that current security approaches often clash with operational realities. A framework of robust security principles and best practices demonstrates how a proactive, multilayered defense strategy can protect critical test assets over the long term. Companies that invest in test system security can strengthen the resilience of their connected test ecosystems.
Test system security is a frontline engineering concern
According to recent research by ABI Research and Palo Alto Networks, 72% of OT attacks originate in an information technology (IT) network. Yet, test systems are hubs that connect OT and enterprise IT networks, making their vulnerabilities potential points of unauthorized access to the IT network. While these networks share risks, they don’t share operational priorities. The traditional security approach of IT delivering security specifications to test design teams doesn’t address OT technology realities. Teams often freeze test systems for months to avoid disruption, delaying patching or validation and leaving known vulnerabilities in place. This is especially problematic for OT assets, where 62% of exploit triggers are tied to vulnerabilities that are six to 10 years old.
The Palo Alto research study also found that 40% of organizations experience friction between their IT and OT teams, creating communication gaps and vulnerabilities that attackers can exploit. Companies that don’t bridge this gap through collaboration will struggle to strengthen their defenses. As OT security transitions from an internal IT concern to a customer expectation and regulatory mandate, failing to align teams on security strategies will jeopardize both compliance and competitiveness. For these reasons, engineers need to become active participants in cybersecurity design decisions and risk mitigation planning to build long-term resilience into their T&M systems.
Where test systems are most vulnerable
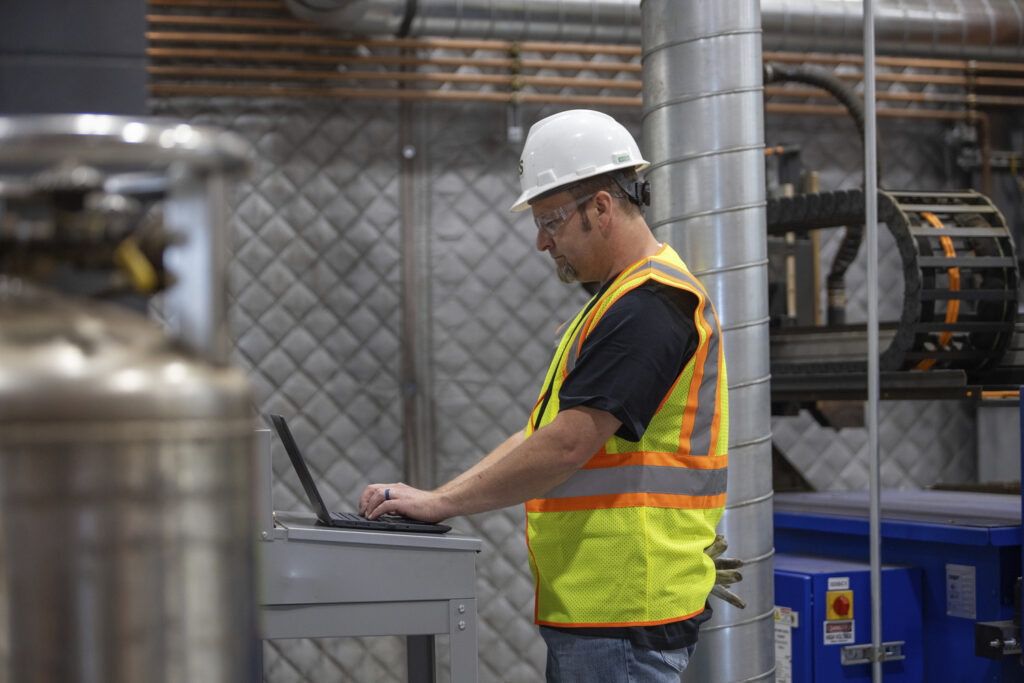
The modern test environment presents multiple attack vectors that don’t exist in isolated systems. Cloud connectivity and remote access capabilities have dramatically expanded the attack surface. They enable operational efficiency but also create entry points for malicious actors. Remote access points, whether through corporate IT networks or direct 4G/5G connections, often operate without full visibility from security teams, creating blind spots in network monitoring.
Vendor compromise is also a significant yet often underappreciated vulnerability in test system security. Malicious code or vulnerabilities can be introduced throughout the supply chain, by the machine builder, at the component level or through third-party suppliers. These compromises are often invisible to the end user. As a result, organizations can inherit security risks that are deeply embedded and difficult to detect.
Legacy systems present unique challenges that contradict common security assumptions. For example, air-gapping didn’t protect Iran’s uranium enrichment systems from the Stuxnet malware, which is believed to have been transmitted via a USB stick. Attackers routinely scan networks for devices, such as outdated switches or computers running systems that have well-documented security flaws. Because many organizations fail to apply patches or cannot update legacy systems, these devices become easy targets.
Then there’s the human element. Social engineering attacks consistently exploit employees who click malicious links or fall for credential-harvesting schemes. Even security-aware personnel make mistakes, highlighting the need for robust training programs and fail-safe system designs as essential components of any comprehensive security strategy. Because no amount of training can eliminate human error entirely, it’s critical to foster a culture of security awareness and to design systems that minimize the impact of inevitable mistakes.
Practical strategies for multilayered system defense
A strong cybersecurity posture for T&M systems depends on layered protections that account for both technical vulnerabilities and operational constraints. No single defensive action is sufficient. Instead, a series of strategies that work together to reduce exposure over time and across system boundaries is more essential:
- Adopt a secure development framework. Frameworks, such as NIST SP 800-218 (Recommendations for Mitigating the Risk of Software Vulnerabilities), provide guidance for integrating security throughout the software development lifecycle. Also, consult NIST frameworks that address various aspects of system defense, including NIST SP 800-171 (Protecting Controlled Unclassified Information in Nonfederal Systems and Organizations) and NIST SP 800-82 (Guide to Operational Technology Security).
- Conduct risk assessments and document an asset inventory. Identify which assets are critical to operations, understand the consequences of compromise and allocate cyber defense resources where they’re needed most.
- Implement zero-trust principles. Zero trust means no implicit trust for any actor on a network. Every user, device or system must verify identity and authorization continuously. This model counters assumptions of safety within internal networks, which attackers often exploit.
- Minimize risks of vendor compromise through the software bill of materials (SBOMs). Vendors use SBOMs to document the components and dependencies built into their software. With this information, companies can identify known vulnerabilities in their vendor software and take action, such as patching and configuration control, to address them.
Together, these practices provide a cybersecurity foundation that includes ongoing monitoring and review of defenses, helping test environments’ security keep up with threats.
Expanding security culture and collaboration
Technical controls alone won’t secure T&M systems. True resilience depends on the human element and developing an organizational culture that treats cybersecurity as a shared responsibility. When OT cybersecurity schemes are developed away from the teams that build, operate and maintain the test systems, the resulting security measures are often impractical and fail to address real-world needs and risks. For example, IT security teams may mandate the closure of certain ports or disable interfaces that are essential to test system operation. These top-down cybersecurity mandates create friction between teams that should be collaborating to secure their test environment.
To overcome this challenge, it’s essential for organizations to foster a problem-solving culture that brings together control engineers, security professionals and operators early in the process. Engineers offer essential insight into system behavior, constraints and operational risk, knowledge that the IT security teams may lack. Embedding that context into security planning from the earliest stages results in more practical and effective protection. These multidisciplinary discussions can include “red teaming” exercises that ask, “How would you attack this system?” to help surface vulnerabilities and practical concerns that might otherwise be missed.
Building a shared responsibility security culture also requires regular, role-specific training for all employees. Phishing simulations and awareness programs can help them recognize their part in defending critical systems. Train team members on what to do when they suspect a threat. Progressing toward cybersecurity maturity involves continuous conversations that normalize vigilance, reinforce accountability and entrench security into the organization’s day-to-day culture.
How regulation drives change
The European Union’s (EU) Cyber Resilience Act (CRA), scheduled to take effect in 2027, will make product cybersecurity a prerequisite for market access, requiring manufacturers to meet defined security criteria before selling to European consumers. Thus, the CRA is expected to become a de facto global standard, influencing practices outside the EU. Manufacturers, regardless of their location, will have to ensure that their products with digital elements comply with the CRA if they want to sell in the EU market.
In the United States, the Department of Defense is taking a more prescriptive approach. A 2025 Department of Defense memorandum mandates compliance with NIST SP 800-171 for all defense contractors under the Defense Federal Acquisition Regulation Supplement (DFARS). This memorandum establishes a contractual obligation for advanced manufacturing companies with defense ties to follow a defined cybersecurity framework.

Ongoing security of T&M systems has long been underfunded and overlooked. Governments increasing the pressure on companies to improve their cybersecurity posture may be the key that unlocks the funding needed to build a robust OT security scheme.
Sustaining cyber defense through culture, funding and teamwork
Modern test systems face sophisticated threats that demand a comprehensive defense strategy. The path forward centers on three critical pillars: proactive risk management, a collaborative security culture and sustainable funding models. The traditional model of upfront project funding ignores the realities of risks that grow and mutate as new cybercriminals and vulnerabilities emerge. Without resources to adapt a T&M system’s security posture over time, even well-designed systems will become exposed. As cybersecurity becomes a prerequisite for deployment, it’s imperative for initial project plans to include long-term funding for maintaining a T&M system’s security throughout its lifecycle.
Because cybersecurity is not a fixed state but a maturing process, it can’t remain the sole responsibility of IT teams. From concept through maintenance, consultation among all system stakeholders is necessary to integrate security resilience as architectures, process flows and risks change. Fundamentally, this requires moving from a compliance-driven approach to a collaborative, proactive security culture.
It’s critical for all stakeholders to view cybersecurity not as a checklist but as an ongoing effort that includes monitoring, training and adaptation. There is no passing a goal line to reach a state of permanent security. Instead, the goal is to create organizational resilience that can respond dynamically to threats while maintaining operational effectiveness.
AUTHOR
Dan Idzikowski is a senior staff engineer, instrumentation and controls for ACS. ACS engineers, integrates and builds technically complex equipment, controls and facilities for industry-leading companies in markets including automotive, aerospace, energy, chemical, manufacturing and more. ACS specializes in control systems, custom machines, testing solutions, automation and production systems, as well as the design and construction of integrated facilities. For more information, please call (608) 663-1590 or visit http://www.acscm.com.
Steve Summers is the security lead for aerospace and defense customers at NI, part of Emerson. For more information, visit ni.com/security.
LEARNING OBJECTIVES
- Understand why increased connectivity in test systems creates new cybersecurity risks across IT and OT environments.
- Identify the key vulnerabilities in modern test and measurement systems, including remote access, supply chain risks, legacy equipment and human error.
- Recognize how multilayered security strategies, cross-team collaboration and emerging regulations strengthen long-term test system resilience.
CONSIDER THIS
How will your organization proactively strengthen test system security across both IT and OT teams before a cyberattack exposes existing vulnerabilities?